

Retail AI leaks sensitive data to unauthorised users
Fri, 2nd Oct 2026 (Today)
Netskope Threat Labs has published research on AI-related security incidents in the retail sector, finding that nearly one in 10 involved AI exposing sensitive data to unauthorised users.
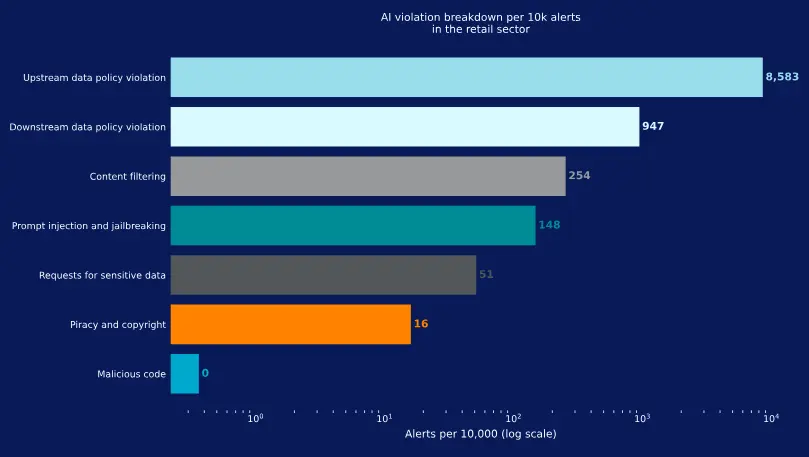
Regulated data, including personal and payment information, accounted for 56% of AI-related data policy violations in the sector. Source code made up 20%, while passwords and API keys represented 16%.
The findings suggest a shift in AI risk patterns for retailers. Alongside concerns about employees submitting sensitive information into AI tools, the research identified downstream violations as the second-largest source of AI security incidents among organisations able to monitor that risk. In these cases, AI systems display protected information to users who should not have access to it.
Those downstream incidents accounted for 9.5% of all AI security alerts in the retail organisations covered by the data.
Account use
The report also found that retailers are trying to bring more employee AI activity under company oversight by rolling out managed accounts. Use of corporate AI accounts rose from 40% to 73%, while use of personal AI accounts for work fell from 70% to 44%.
Even so, personal use remains widespread. The share of employees switching between personal and enterprise AI accounts increased from 11% to 18%, suggesting the boundary between personal and company use is becoming less distinct.
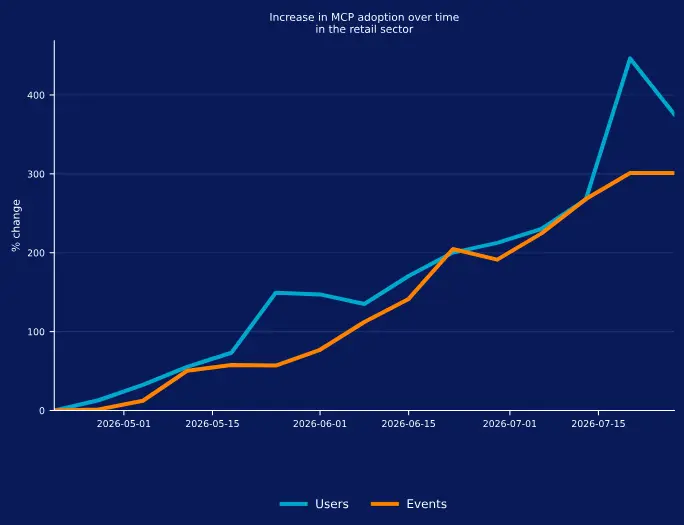
The technical environment around AI is also becoming more complex. The number of AI agents interacting with remote Model Context Protocol servers increased by about 400%, while MCP-related events rose by around 300%.
MCP connections allow AI systems to interact with internal and external tools and data sources. That trend offers retailers a clearer sign of how quickly AI agents are being deployed in business environments and increases the need to understand what information those systems can access.
Malicious activity
Outside data governance, the research recorded a sharp rise in AI-linked cyber threats. AI-themed malicious lure activity increased 400% between December 2025 and March 2026.
Retail employees also encountered and clicked malicious links returned by AI applications at rates ranging from about 40 to more than 160 per 100,000 users each week, according to the findings.
The report identified Particular Audience as the most frequently blocked AI application, restricted by 46% of retail organisations in the dataset. ZeroGPT followed at 37%, while Landbot and DeepSeek were each blocked by 34% of organisations.
Use of mainstream AI platforms remained widespread across the sector. Anthropic Claude Platform was used by 96% of retail organisations in the dataset, ahead of ChatGPT at 84%, while Claude Code reached 83%.
The research was based on aggregated usage data collected through the Netskope One platform from a subset of retail customers over a 15-month period.
Gianpietro Cutolo, Cloud Threat Researcher at Netskope, said the findings reflect a broader shift as retailers push AI into day-to-day operations.
"Retailers are moving beyond simply experimenting with AI and are starting to embed it across everyday operations, customer experiences, and business workflows," said Gianpietro Cutolo, Cloud Threat Researcher at Netskope.
"But as AI becomes more deeply connected to the data and systems that power the retail business, the risks become harder to separate from the opportunities. The challenge is no longer deciding whether to use AI, but making sure it can be used at the speed the business demands without losing control of sensitive customer and company data. Retailers that can combine rapid AI adoption with strong visibility and governance will be best placed to turn AI into a competitive advantage without creating unnecessary risk."